ISO and GRC support for organizations operating in Saudi Arabia.
Organizations in Saudi Arabia can face overlapping expectations from customers, standards, contracts, regulators and internal governance.
Supporting organizations across Saudi Arabia, ISOReadyHub delivers practical ISO management-system and GRC implementation with an evidence-first approach.
Support can include
- Scope and context
- Gap assessment
- Implementation planning
- Governance and management-system documentation
- Operating controls
- Evidence
- Internal readiness
- Certification support
Relevant standards may include
Applicability is confirmed rather than assumed.
We help organizations identify potentially applicable regulatory, contractual and customer requirements as part of scope and readiness work. Screening lists the instruments that could be relevant to the organization’s activities, sector, customers, data and obligations, records why each was flagged, and names who will verify whether it applies. Areas often screened include:
- PDPL / SDAIA
- Personal Data Protection Law; Saudi Data & Artificial Intelligence Authority
- CST
- Communications, Space & Technology Commission
- SAMA
- Saudi Central Bank
- Government and tenders
- Government or tender obligations
- Sector
- Sector-specific requirements
- Contracts
- Customer contracts
What a screening record captures
Each screening entry records the instrument, potential trigger, applicability status, requirement owner, evidence and action required.
Illustrative template — not client evidence
| Field | Illustrative entry |
|---|---|
| Instrument | Personal Data Protection Law (PDPL) |
| Potential trigger | Processing personal data relating to individuals in Saudi Arabia |
| Applicability status | Potentially applicable – confirm |
| Requirement owner | Data protection lead |
| Evidence | Processing inventory and documented applicability assessment |
| Action required | Obtain qualified Saudi legal advice on whether and how it applies |
How we deliver in Saudi Arabia
ISOReadyHub leads the advisory engagement, while Saudi-based coordination and business support are provided through a registered local establishment in Jeddah. The delivery model keeps engagement leadership, local support and independent certification responsibilities clearly separated.
-
ISOReadyHub advisory delivery
ISO management systems, cybersecurity, GRC, readiness and evidence-focused implementation under the agreed engagement scope.
-
Saudi-based coordination
Local stakeholder engagement, executive coordination and business support through Ahmed Zaidan Management Consulting Office.
-
Independent certification
Where certification is required, the certification decision remains with an independent, appropriately accredited certification body.
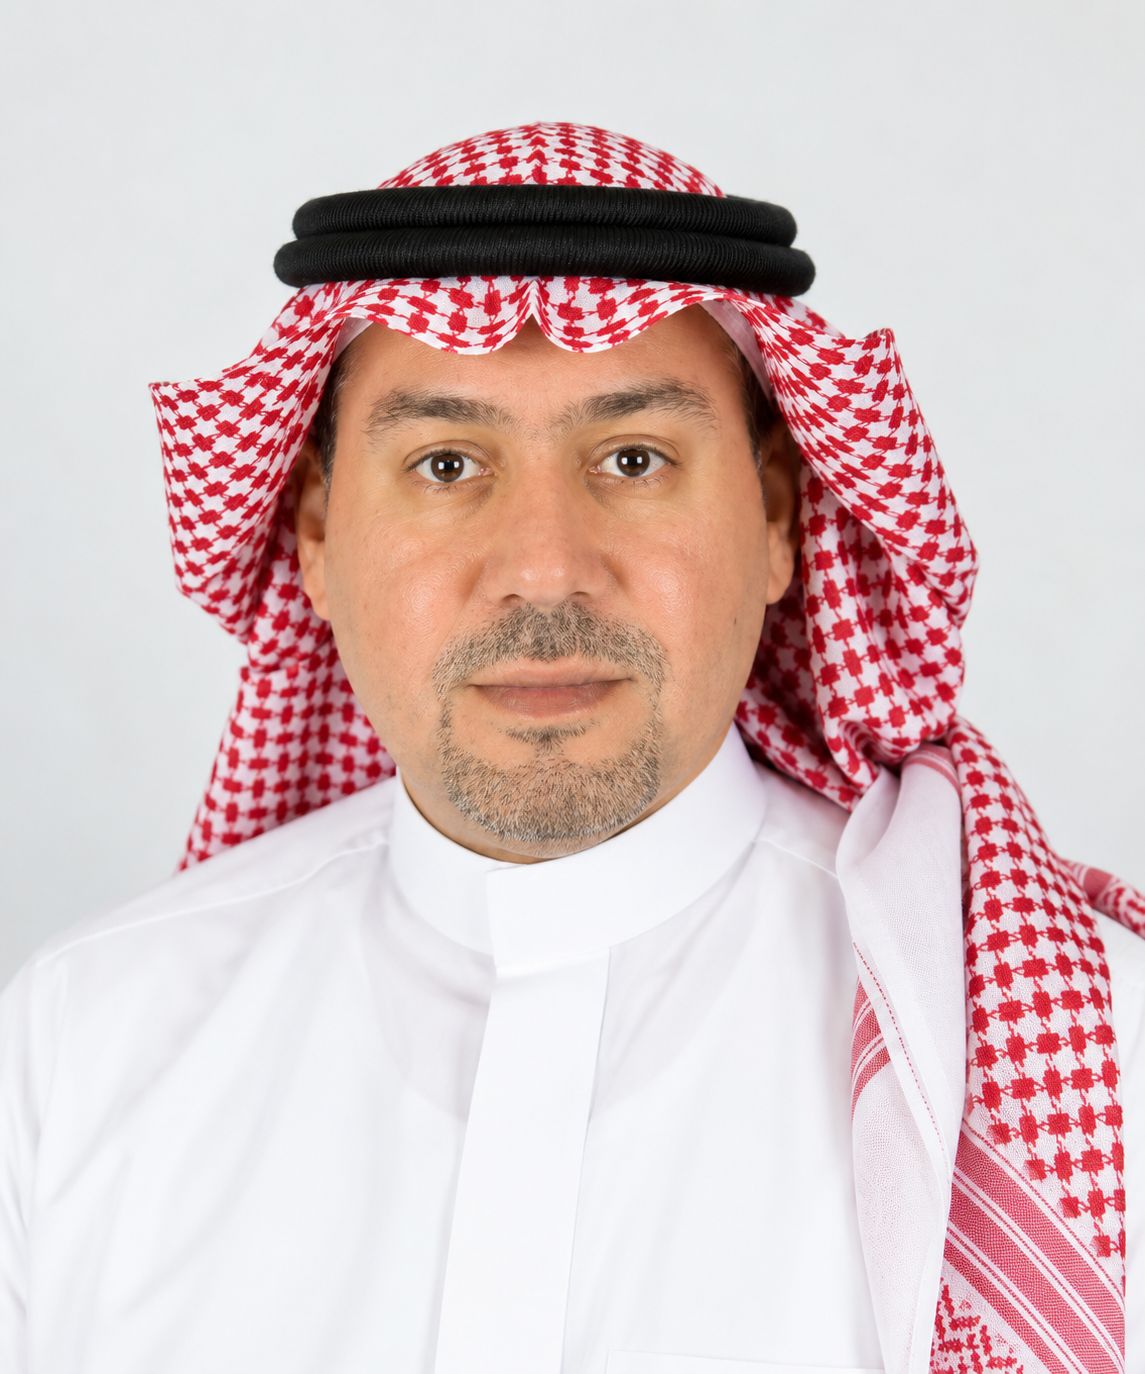
Ahmed M. Zaidan
Saudi Business & Advisory Lead
Ahmed brings 28 years of executive leadership and management consulting experience across strategy, transformation, operational improvement, governance and organizational effectiveness. His background includes CEO roles, 14 years as Managing Partner of United Arabia Consulting, and earlier consulting experience with Arthur Andersen in Jeddah.
Within ISOReadyHub’s Saudi delivery model, Ahmed supports local client engagement, executive stakeholder coordination and business advisory, helping connect management-system requirements with the practical realities of operating organizations in the Kingdom.
Saudi establishment
Ahmed Zaidan Management Consulting Office
Jeddah, Saudi Arabia
Registered Saudi individual establishment supporting local engagement and delivery coordination for agreed assignments in the Kingdom.
Registration information available for verification.
Industries we can support in Saudi Arabia
ISO management systems, cybersecurity and GRC requirements vary by sector, operating model, customer expectations and regulatory context. ISOReadyHub can support organizations across a range of industries, with scope and applicable requirements confirmed during discovery.
- Technology, software & digital services
- Professional & business services
- Industrial & manufacturing
- Construction, engineering & project-based businesses
- Retail, distribution & e-commerce
- Healthcare & regulated service providers
The applicable ISO standards, cybersecurity requirements and regulatory obligations depend on the organization’s sector, services, customers, data environment and contractual requirements. Applicability is confirmed during discovery rather than assumed.
Planning ISO or GRC work in Saudi Arabia?
Start with a focused discovery conversation to confirm scope, applicable requirements, delivery responsibilities and the path to readiness.