Management systems that work. Assurance you can prove.
We help growing technology, services and industrial organisations turn ISO, cybersecurity and governance requirements into clear ownership, working controls and evidence that can withstand review.
- Requirement Suppliers that affect quality are evaluated
- Control Annual supplier evaluation against agreed criteria
- Owner Procurement lead
- Evidence Completed evaluations and approved-supplier list
- Monitoring Quarterly delivery and defect data
- Review Input to management review
Three connected capabilities
We work across ISO management systems, cybersecurity and governance, risk and compliance. The focus is not on producing a binder for audit day. It is on helping the organization understand what applies, close meaningful gaps, implement workable processes and controls, and prove that they operate.
-
ISO Management Systems
ISO Management Systems: Explore ISO standardsBuild, improve and integrate management systems around internationally recognized standards.
- Scope definition
- Gap assessment
- Implementation planning
- Process and control design
- Operating evidence
- Internal readiness
- Certification support
-
Cybersecurity & Technical Assurance
Cybersecurity & Technical Assurance: Explore cybersecurityStrengthen security where governance and technology meet. Typical work includes:
- Security governance
- Identity and access review
- Cloud and infrastructure control review
- Vulnerability-management process review
- Resilience assessment
- Coordination of qualified technical specialists
-
Governance, Risk & Compliance
Governance, Risk & Compliance: Explore GRCCreate clearer accountability, stronger risk decisions and more defensible assurance.
- Governance
- Risk management
- Policy frameworks
- Compliance obligations
- Supplier assurance
- Privacy considerations
- Evidence-based oversight
Standards we support
Each standard provides a management framework. The value comes from how the system is implemented, used and evidenced.
- Last verified
- Status
- Edition status last reviewed
-
ISO 9001 — Quality Management
Consistent delivery, customer focus, process control, performance evaluation and continual improvement.
Current edition ISO 9001:2026 (September 2026)
-
ISO 14001 — Environmental Management
Environmental aspects, obligations, objectives, operational controls and measurable performance.
Current edition ISO 14001:2026 (April 2026)
-
ISO 45001 — Occupational Health & Safety
OH&S risks, worker participation, legal requirements, operational control and improvement.
ISO 45001:2018 current; revision at Draft International Standard stage
-
ISO/IEC 27001 — Information Security
Risk-based information security management, risk treatment, controls, evidence and continual improvement.
ISO/IEC 27001:2022 with Amendment 1:2024
-
ISO 22301 — Business Continuity
Disruption impact, continuity priorities, response, recovery, exercising and improvement.
ISO 22301:2019 with Amendment 1:2024; under revision
A policy describes what should happen. Evidence demonstrates what actually happens.
Our delivery model moves from understanding the organization to proving that its system operates.
-
Step 1: Discover
Understand objectives, services, systems, stakeholders, obligations and intended outcomes.
-
Step 2: Assess
Identify requirements, gaps, dependencies, risks and evidence weaknesses.
-
Step 3: Implement
Design proportionate processes and controls using existing systems where they are effective.
-
Step 4: Prove
Build and organize evidence from real operations.
-
Step 5: Assure
Prepare for internal review, customer assurance and independent certification.
- Founder experience More than three decades of business experience
- Evidence-first delivery Working controls, accountable ownership and reviewable evidence
- Certification independence ISOReadyHub does not issue ISO certificates
- Illustrative deliverables Public sample structures are available for review
What clients typically receive
Depending on scope, an engagement can produce the outputs listed here.
The evidence chain keeps scope, implementation and readiness testing anchored to work that can be owned, observed and reviewed.
For ISO/IEC 27001 work, outputs can also include a risk treatment plan and Statement of Applicability.
See illustrative sample deliverablesGovernance & Scope
- Agreed scope and implementation boundaries
- Management-system framework
- Policies and procedures where required
Risk & Controls
- Structured gap register
- Risk methodology and risk register
- Remediation plan with owners and dates
Evidence & Assurance
- Evidence register
- Management-review inputs
Readiness & Certification Support
- Internal-readiness plan
- Certification-readiness action plan
Organizations do not all need the same programme.
The right model depends on scope, maturity, target outcome, internal capability, remediation effort and evidence readiness.
Compare engagement models and what drives cost- Readiness Assessment
- A defensible view of where you stand before committing to a wider programme.
- Implementation Programme
- Building or materially improving the management system.
- Readiness + Certification Support
- For organizations targeting independent certification.
- Ongoing Advisory
- Continued ISO and GRC support after implementation.
- Specialist Technical Assurance Coordination
- Work that requires specialist technical capability or independence.
Industry context matters
The same ISO requirement can look very different in a SaaS company, professional-services firm, manufacturer or healthcare organization.
-
Technology & SaaS
Technology & SaaS: Technology & SaaS approachCloud services, identity, secure development, production access, resilience, suppliers and customer assurance.
-
Professional Services
Professional Services: Professional Services approachService quality, information handling, remote work, client requirements, supplier risk and scalable governance.
-
Manufacturing & Industrial
Manufacturing & Industrial: Manufacturing & Industrial approachQuality, maintenance, safety, environment, suppliers and continuity, integrated with operational processes.
-
Healthcare
Healthcare: Healthcare approachQuality, information security, privacy, availability, supplier and operational requirements together.
ISO and GRC support for organizations operating in Saudi Arabia
We support organizations operating in Saudi Arabia with ISO management systems and GRC advisory.
Which Saudi regulatory and contractual requirements are relevant depends on the organization’s activities, sector, customers, data and obligations, and is confirmed rather than assumed.
ISO and GRC advisory in Saudi Arabia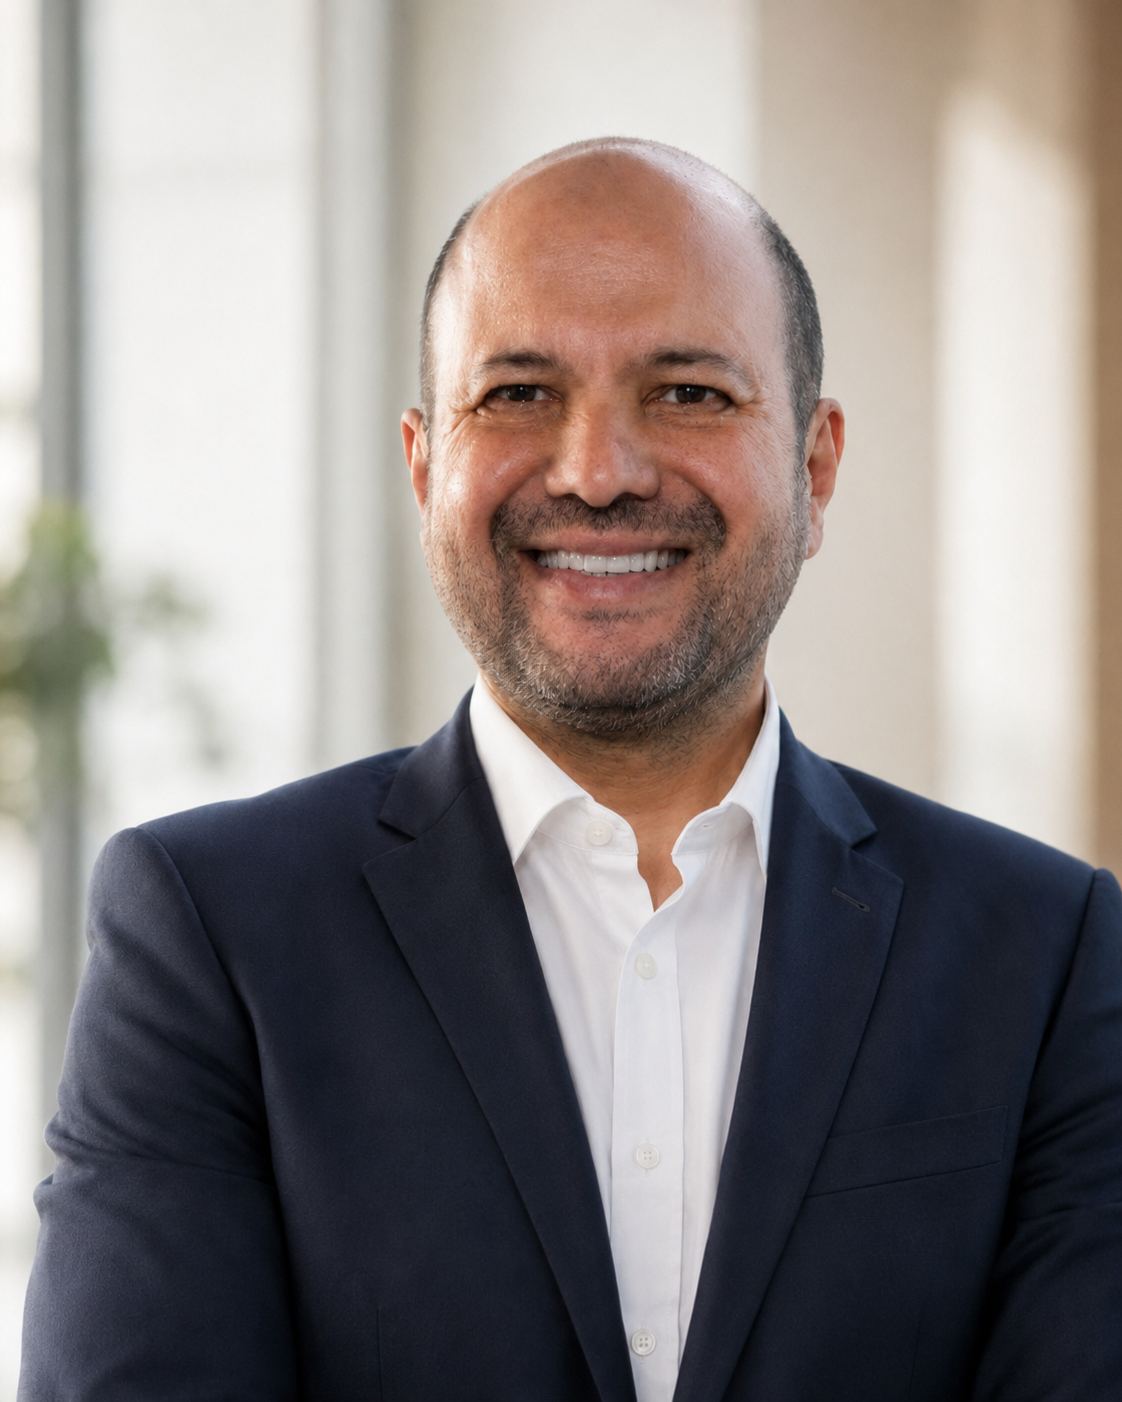
Eng. Yasser M. Zaidan
Founder & Principal Consultant, ISOReadyHub
Yasser brings more than three decades of business experience across technology, telecommunications, distribution, manufacturing and digital operations.
His operating perspective is practical: management systems should improve how an organization runs, not exist only for an audit.
Start with a focused discovery conversation
Tell us what you are trying to achieve, what is driving the requirement and where you are today. We use the first discussion to clarify scope and next steps, not to force a predefined package.